信任
安全与隐私
Carnet 如何依据 GDPR 处理您的零售商数据。
最后更新:
角色
对于您的零售商的订单详情,您(品牌)是控制者,Carnet 是您的处理者,双方签订我们的数据处理协议。对于您自己的账户数据,Carnet 是控制者。
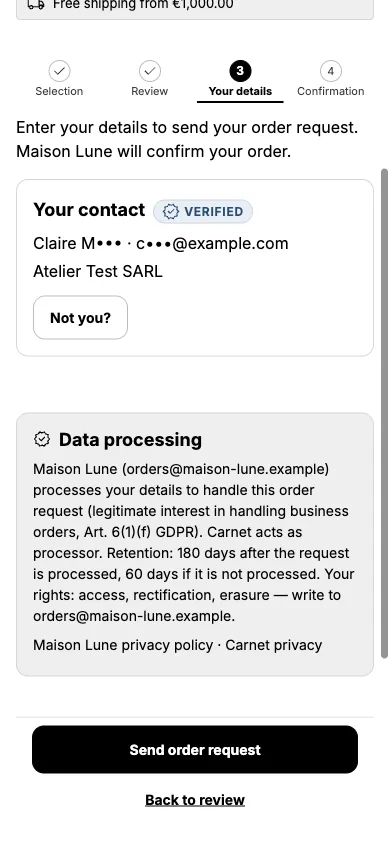
买家在订单页面上看到的声明会写明品牌名称,并提供 privacy@ordersheet.net。
我们存储什么
- 您创建的产品册和链接
- 订单请求:订单行、数量、编号
- 买家联系方式:姓名、邮箱、公司,以及对方提供的电话
- 不存储银行卡或支付数据:支付留在 Shopify 内
保护措施
- 买家联系方式、邮件收件人和链接令牌均静态加密,每个商店使用独立密钥。订单行不加密。
- 带签名的链接,可暂停或撤销
- 每个公开链接每 24 小时有访问频率限制
- 自动处理 Shopify 的 GDPR 请求(客户数据请求、客户数据删除、商店数据删除)
- 有限的 Shopify 访问权限:Carnet 读取商品、主题、市场、语言和客户(用于匹配零售商),并创建草稿订单。它不会编辑您的主题,也不会读取您的订单或库存。请参阅下表。
设置与权限
以下是 Carnet 在安装时请求的全部 Shopify 访问权限范围。
| 权限范围 | Carnet 的用途 |
|---|---|
read_products | 读取您的商品、图片和变体,用于生成产品册 |
read_customers | 读取客户,用于匹配零售商 |
write_draft_orders | 根据零售商的订单创建草稿订单 |
read_markets, read_locales, read_translations | 读取您的市场、商店语言和翻译,用于买家页面 |
read_themes | 读取您主题的颜色和字体,用于主题导入。Carnet 对主题没有写入权限:不会编辑您的主题。 |
write_app_proxy | 让买家链接在您商店自己的域名下的 /apps/carnet 打开(Shopify 的应用代理),使链接看起来就像您商店的链接 |
Carnet 没有读取您的订单或库存的权限范围。
保留期限
| 数据 | 保留时长 |
|---|---|
| 订单请求详情 | 处理后 180 天(若从未处理,则为 60 天) |
| 邮件正文 | 发送后 7 天 |
| 备份 | 备份保留加密副本,直至过期(35天) |
| 卸载后 | 按照 Shopify 的数据删除请求予以删除(2天) |
子处理者
| 服务商 | 用途 |
|---|---|
| Shopify | 平台 |
| Microsoft Azure | 托管、数据库、邮件(区域:France Central) |
| Cloudflare | 网络和买家链接主机 |
Security incidents
Carnet has a written incident response policy. The operator leads every incident, from detection to review.
- Detection: production errors raise an automatic alert, and we act on notices from Shopify and our hosting providers.
- Containment first: we can rotate encryption and session keys, revoke third-party access tokens and take the app offline.
- Notification: if a personal data breach affects your data, we email you without undue delay after we become aware of it, at the contact address registered for your shop in Shopify. The email says what happened, which data and how many records are affected, the likely consequences and what we are doing. It gives you what you need to meet your own duties under Articles 33 and 34 of the GDPR, including the 72-hour deadline to notify your supervisory authority. We also inform Shopify, as its partner program requires.
- After every incident we write a review with the cause and the fixes, and we test the procedure at least once a year.
Who has read your buyers' data
Every time buyer contact data (name, email, phone, address) is decrypted, by you or your staff in the Carnet admin, or by a background job such as sending a recap email or creating a draft order, Carnet records when, for which store, which staff member or job, and which request. The record never contains the data itself. Entries are kept for 365 days, then deleted, and are deleted with the rest of your store's data on uninstall. Only the Carnet operator can read the log, directly in the database.