신뢰
보안 및 개인정보 보호
Carnet이 GDPR에 따라 거래처의 데이터를 처리하는 방식입니다.
마지막 업데이트:
역할
거래처의 주문 정보에 대해서는 사용자(브랜드)가 컨트롤러이고 Carnet은 데이터 처리 계약에 따른 프로세서입니다. 사용자 본인의 계정 데이터에 대해서는 Carnet이 컨트롤러입니다.
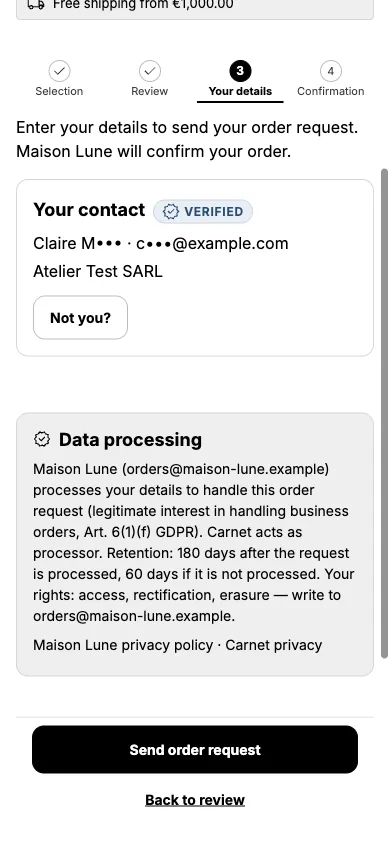
구매자가 주문 페이지에서 보는 안내에는 브랜드 이름이 표시되며 privacy@ordersheet.net이(가) 안내됩니다.
저장하는 데이터
- 사용자가 만든 시트와 링크
- 주문 요청: 품목, 수량, 참조 번호
- 구매자 연락처: 이름, 이메일, 회사, 입력한 경우 전화번호
- 카드 또는 결제 데이터 없음: 결제는 Shopify에서 이루어집니다
보호
- 구매자 연락처, 이메일 수신자, 링크 토큰은 스토어마다 다른 키로 저장 시 암호화됩니다. 주문 품목은 암호화되지 않습니다.
- 일시 중지하거나 취소할 수 있는 서명된 링크
- 공개 링크마다 24시간 단위로 요청 횟수 제한
- Shopify의 GDPR 요청(고객 데이터 요청, 고객 데이터 삭제, 스토어 데이터 삭제)을 자동으로 처리
- 제한된 Shopify 접근: Carnet은 상품, 테마, 마켓, 언어, 고객(거래처를 맞추기 위해)을 읽고 임시 주문을 생성합니다. 테마를 수정하지 않으며 주문이나 재고를 읽지 않습니다. 아래 표를 참고하세요.
설정 및 권한
설치 시 Carnet이 요청하는 Shopify 접근 범위는 아래가 전부입니다.
| 접근 범위 | Carnet의 사용 목적 |
|---|---|
read_products | 라인 시트를 만들기 위해 상품, 이미지, 옵션을 읽습니다 |
read_customers | 거래처를 맞추기 위해 고객을 읽습니다 |
write_draft_orders | 거래처의 주문으로 임시 주문을 생성합니다 |
read_markets, read_locales, read_translations | 구매자 페이지를 위해 마켓, 스토어 언어, 번역을 읽습니다 |
read_themes | 테마 가져오기를 위해 테마의 색상과 글꼴을 읽습니다. Carnet에는 테마 쓰기 권한이 없으므로 테마를 수정하지 않습니다. |
write_app_proxy | 구매자 링크가 스토어 자체 도메인의 /apps/carnet 경로(Shopify 앱 프록시)에서 열리게 하여 링크가 스토어의 링크처럼 보이게 합니다 |
Carnet에는 주문이나 재고를 읽는 권한 범위가 없습니다.
보관 기간
| 데이터 | 보관 |
|---|---|
| 주문 요청 정보 | 처리 후 180일(처리되지 않은 경우 60일) |
| 이메일 본문 | 발송 후 7일 |
| 백업 | 백업은 만료될 때까지 암호화된 사본을 보관합니다(35일) |
| 제거 후 | Shopify의 데이터 삭제 요청에 따라 삭제됩니다(2일) |
하위 처리자
| 제공업체 | 목적 |
|---|---|
| Shopify | 플랫폼 |
| Microsoft Azure | 호스팅, 데이터베이스, 이메일(지역: France Central) |
| Cloudflare | 네트워크 및 구매자 링크 호스트 |
Security incidents
Carnet has a written incident response policy. The operator leads every incident, from detection to review.
- Detection: production errors raise an automatic alert, and we act on notices from Shopify and our hosting providers.
- Containment first: we can rotate encryption and session keys, revoke third-party access tokens and take the app offline.
- Notification: if a personal data breach affects your data, we email you without undue delay after we become aware of it, at the contact address registered for your shop in Shopify. The email says what happened, which data and how many records are affected, the likely consequences and what we are doing. It gives you what you need to meet your own duties under Articles 33 and 34 of the GDPR, including the 72-hour deadline to notify your supervisory authority. We also inform Shopify, as its partner program requires.
- After every incident we write a review with the cause and the fixes, and we test the procedure at least once a year.
Who has read your buyers' data
Every time buyer contact data (name, email, phone, address) is decrypted, by you or your staff in the Carnet admin, or by a background job such as sending a recap email or creating a draft order, Carnet records when, for which store, which staff member or job, and which request. The record never contains the data itself. Entries are kept for 365 days, then deleted, and are deleted with the rest of your store's data on uninstall. Only the Carnet operator can read the log, directly in the database.
문의
판매자: hello@ordersheet.net. 구매자: privacy@ordersheet.net.